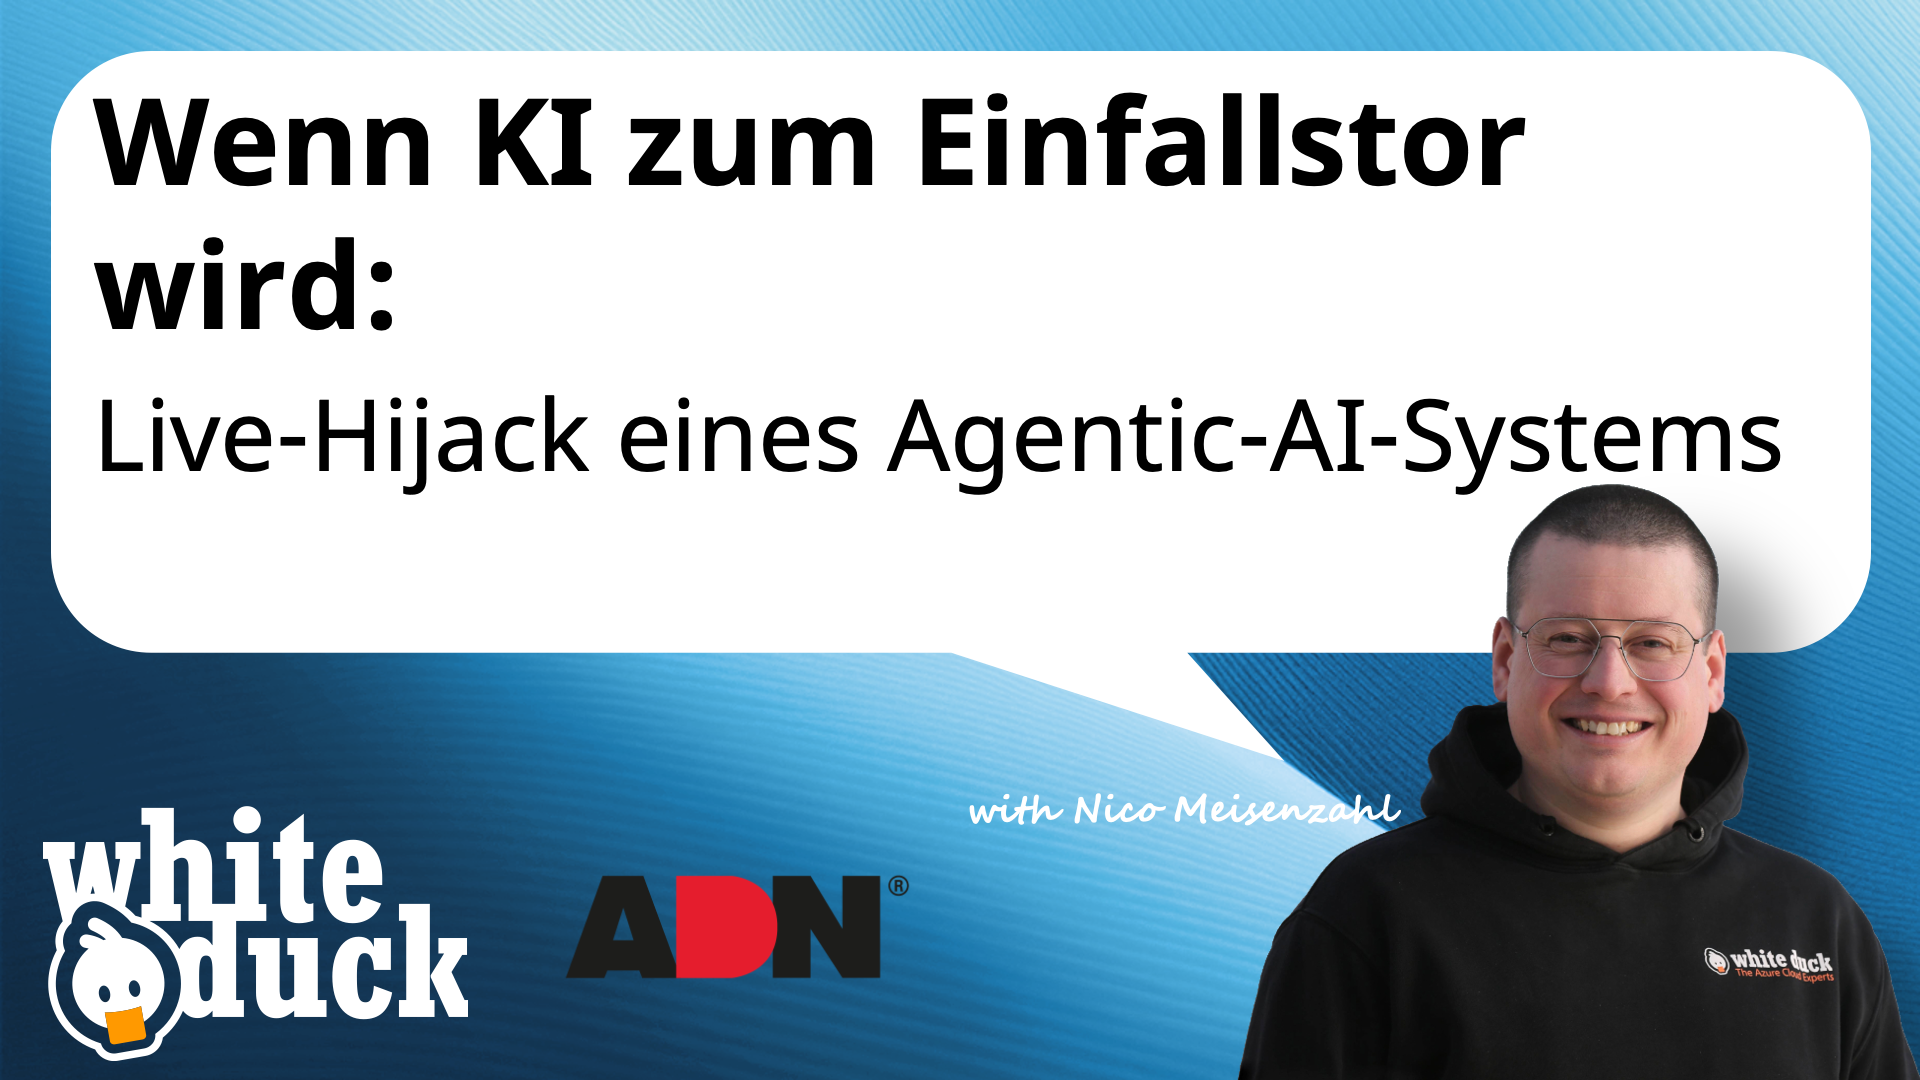
When AI Becomes a Gateway – Live Hijack of an Agentic AI System
Agentic AI is increasingly taking over central tasks in modern platforms – from tool usage to the automation of complete workflows. This new autonomy brings enormous opportunities, but also opens up entirely new attack surfaces.
In this session, we demonstrate in a guided live demo how an Agentic AI system can be compromised step by step. Using practical scenarios, we make typical vulnerabilities visible: manipulated inputs, poisoned knowledge sources, and abused integrations that can lead to unwanted actions and data exfiltration – and why traditional AppSec reaches its limits here.
Speakers:
Nico Meisenzahl (COO, white duck)
Other interesting events